
Cybersecurity in France: a turning point for SMEs and mid-market companies
Cybersecurity in France: a bill transposes DORA, NIS2 and CER. Up to 15,000 SMEs and mid-market firms face new obligations and penalties. Is yours ready?
Stricter regulation for a fast-growing risk
On 15 October 2024, a cybersecurity bill was put before the French Senate. Tabled by Ms Chappaz, the Minister Delegate for Artificial Intelligence and Digital Affairs, the bill transposes three European directives: DORA, NIS2 and CER.
What does this mean?
From now on, 500 to 15,000 companies could be subject to these requirements. This covers 18 sectors of activity, including finance, telecommunications, energy and transport.
Among the new obligations, companies will have to adopt stronger protection measures and report any security incident. In the event of a breach, financial penalties of up to 2% of turnover will be considered.
This initiative comes as cyber threats reach an unprecedented level.
In 2024, cyberattacks rose by 15%, hitting large groups such as Auchan and Free as well as SMEs and subcontractors. The latter have become prime targets for cybercriminals.
SMEs and mid-market companies are prime targets for cybercriminals
While large companies have significantly strengthened their cybersecurity in recent years, SMEs sometimes find it harder to invest in cybersecurity and are ideal entry points for targeting larger organisations.
According to cybermalveillance.gouv.fr, France’s national cybercrime assistance platform, only 22% of SMEs feel ready to face a cyberattack, while 65% admit they are unable to assess the consequences.
Yet the figures speak for themselves: ransomware now accounts for 37% of cyberattacks affecting SMEs, with potentially disastrous consequences:
- Business interruption
- Loss of sensitive data
- Reputational damage
Faced with this reality, the question is no longer whether an SME will be attacked, but when.
Strengthening cybersecurity: an operational and strategic necessity
It is impossible to ignore the threats looming, and yet many still turn a blind eye to this reality. Indeed, investing in cybersecurity is often perceived as expensive.
Yet securing your organisation does not necessarily mean investments beyond your reach.
Some simple measures already make it possible to considerably strengthen resilience against attacks:
- Regularly update software and operating systems to fix known vulnerabilities
- Adopt multi-factor authentication (MFA) to limit the risk of account takeover
- Train employees on the risks of fraudulent emails and phishing attempts
- Regularly back up critical data to an external, disconnected medium
- Monitor network access and detect unusual behaviour
- Avoid using uncertified or pirated software, which is often a malware vector
Everyone is affected by cybersecurity
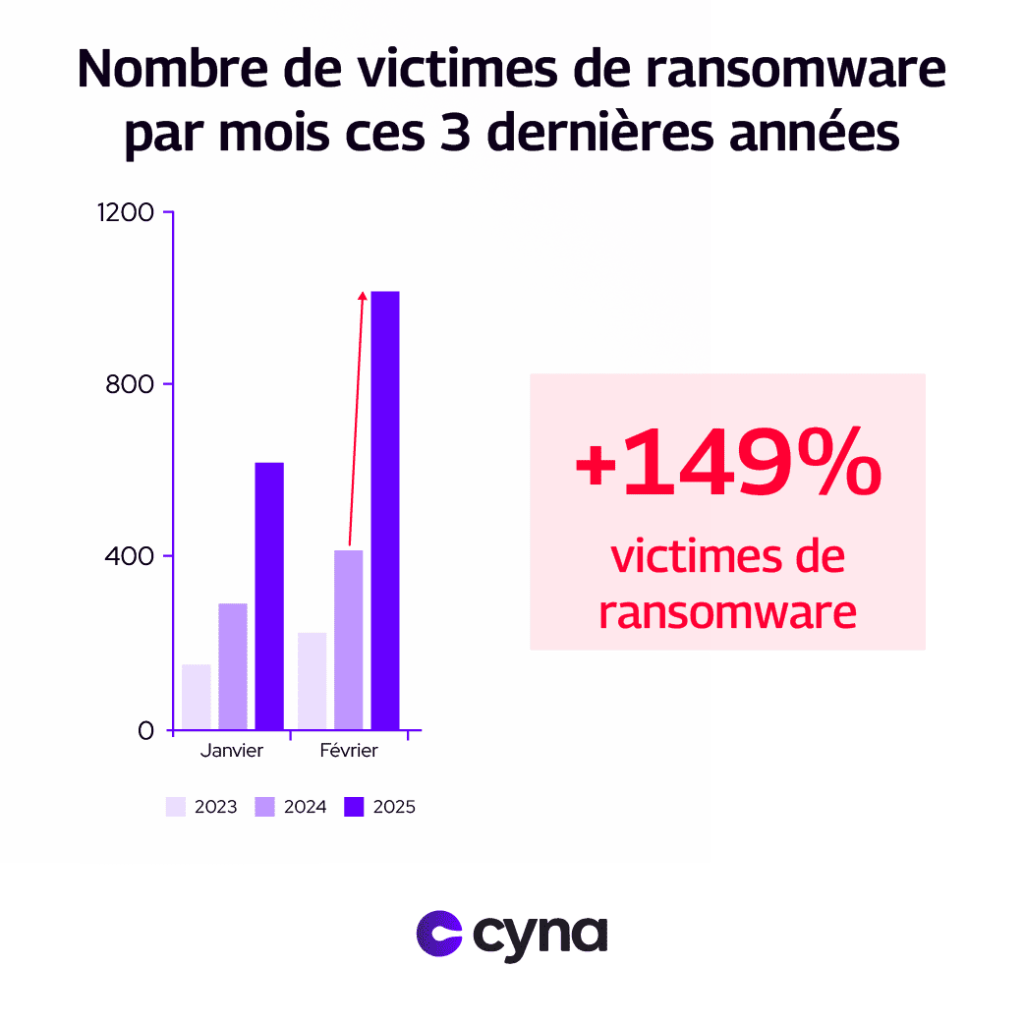
We wanted to come back to the statistics published by the site Ransomware.live, which are rather alarming. While these figures do not cover only France and SMEs, they say a lot about our awareness of risks. The more alert we are to threats, the better we can protect ourselves, both personally and professionally.
What to do in the event of an incident?
If you suffer a cyberattack, how quickly you react is decisive.
We strongly advise you to:
- Immediately isolate the compromised systems
- Alert a cybersecurity expert
- Report the attack to the relevant authorities
These three actions help limit the impact. And above all, do not wait to contact or call us, our CERT can step in quickly.
We also urge you not to give in to ransomware: paying a ransom guarantees nothing, puts you in a position of weakness and fuels the criminal economy.
Key takeaways
The extension of cybersecurity obligations to SMEs should therefore not be seen as a constraint, but as an opportunity to get organised against cyber threats.
Be aware that affordable solutions exist to protect you and prevent cyberattacks as far as possible.
At Cyna, we support SMEs and MSPs in putting effective, tailored solutions in place.
Our approach relies on advanced protection systems and incident response expertise, allowing companies to secure their business without excessive complexity.
Attacks will continue to evolve. The real question is therefore: is your company ready to face them?
If you would like to discuss this with an expert, get in touch.
This article provides general information for guidance only. It is neither legal advice nor a contractual commitment from Cyna: service terms are those of the contract agreed through your partner MSP. For any regulatory question, consult your legal adviser.