
Lessons learned from the cyberattacks handled by the Cyna SOC and CERT in 2025
Webinar hosted by Nathan Bramli: a look back at the most frequent cyberattacks handled by the Cyna SOC and CERT in 2025, and how each one was resolved.
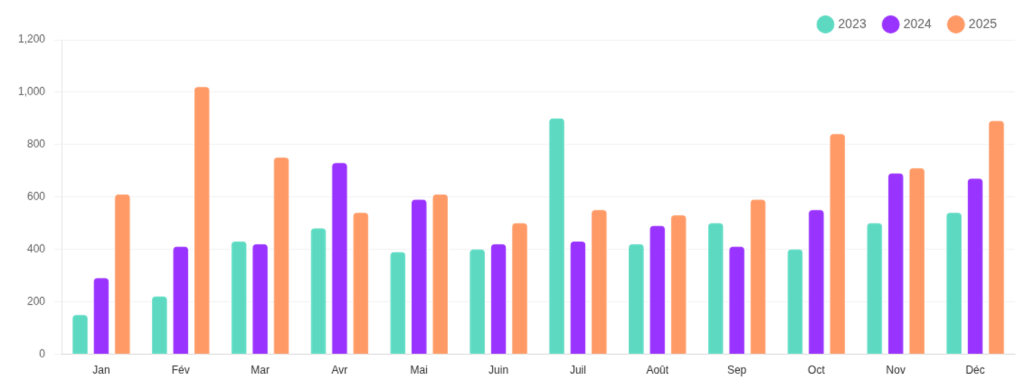
What were the most frequent cyberattacks of 2025?
Join our next webinar, hosted by Nathan Bramli, Head of Cyber at Cyna.
You will look back over 2025 to discover the types of attack most observed over the past year.
We will present the most frequent cases of cyberattacks encountered by our SOC and our CERT, and how we resolved them.
A format that takes you behind the scenes of our teams, 100% concrete and operational, to help you avoid it happening to you.
This webinar is for you if:
- You are an MSP / managed service provider
- You already manage a substantial fleet of endpoints
- You want to better understand attackers so your clients do not get attacked
- You want to protect your SME and mid-market clients more robustly without heavy investment
Webinar programme
- The types of attack most observed during 2025
- The preferred methods attackers use against SMEs and mid-market companies
- The configuration and monitoring errors that open the door to cybercriminals
- Concrete cases of compromises stopped
A year of 2025 rich in lessons
By taking part in this webinar, you will leave with a clear view of the real threats your clients faced. We will give you real attack cases and the keys to protect yourself against them.
If you want to strengthen your credibility with your clients, don’t wait any longer.
Register now.
This article provides general information for guidance only. It is neither legal advice nor a contractual commitment from Cyna: service terms are those of the contract agreed through your partner MSP. For any regulatory question, consult your legal adviser.